Skip to content
AI Goat - AI Security Playground AI GoatTM
v2.0 Read the release announcement

What is AI GoatTM?

Attack real AI systems. Prove what stops them.

AI Goat (AIGoat) is a free, open source, intentionally vulnerable AI-powered shop for learning AI security by doing. Version 2.0 takes the attacks past the chatbot, into retrieval pipelines, MCP servers and tool-calling agents with memory. Exploit each one, then replay it at three defense levels and see which controls actually hold.

LLM labs
23
MCP labs
11
Agentic labs
12
AI Goat v2.0 Attack Labs hub with framework tabs for OWASP LLM 2026 (23 labs), MCP 2025 (11 labs) and Agentic 2026 (12 labs), and the LLM01 to LLM10 risk list
Real v2.0 screens: the Attack Labs hub.

The story

Why we built AI Goat

Companies are shipping LLM chatbots, knowledge assistants, MCP integrations and autonomous agents faster than they can test them. Most teams have never tried the attacks that are unique to AI systems: prompt injection, RAG poisoning, tool poisoning, goal hijack or memory poisoning.

Traditional web security tools don't cover these attack surfaces. A SQL injection scanner won't find a poisoned MCP tool description, and reading about an agent kill chain is not the same as running one.

AI Goat gives you a real, working application with real AI vulnerabilities to attack, study and defend. It runs on your laptop: no cloud bills, no rate limits, and no data leaving your machine.

Built by security practitioners

Created by the AI Security Consortium for people who learn best by doing.

Mapped to three OWASP Top 10 lists

Every lab maps to the OWASP Top 10 for LLM Applications (2026), Agentic Applications (2026) and the MCP Top 10.

Local and free

Apache 2.0 platform code. No signup, no cloud, no API keys. Set it up once and you're ready.

What you get

Core features of AI Goat v2.0

  • 46 labs

    Hands-on attack labs on four surfaces

    23 LLM and RAG labs, 11 MCP labs and 12 agentic AI labs. Each one has a goal, example payloads and the expected result at every defense level.

  • MCP01โ€“MCP10

    Real MCP client and servers

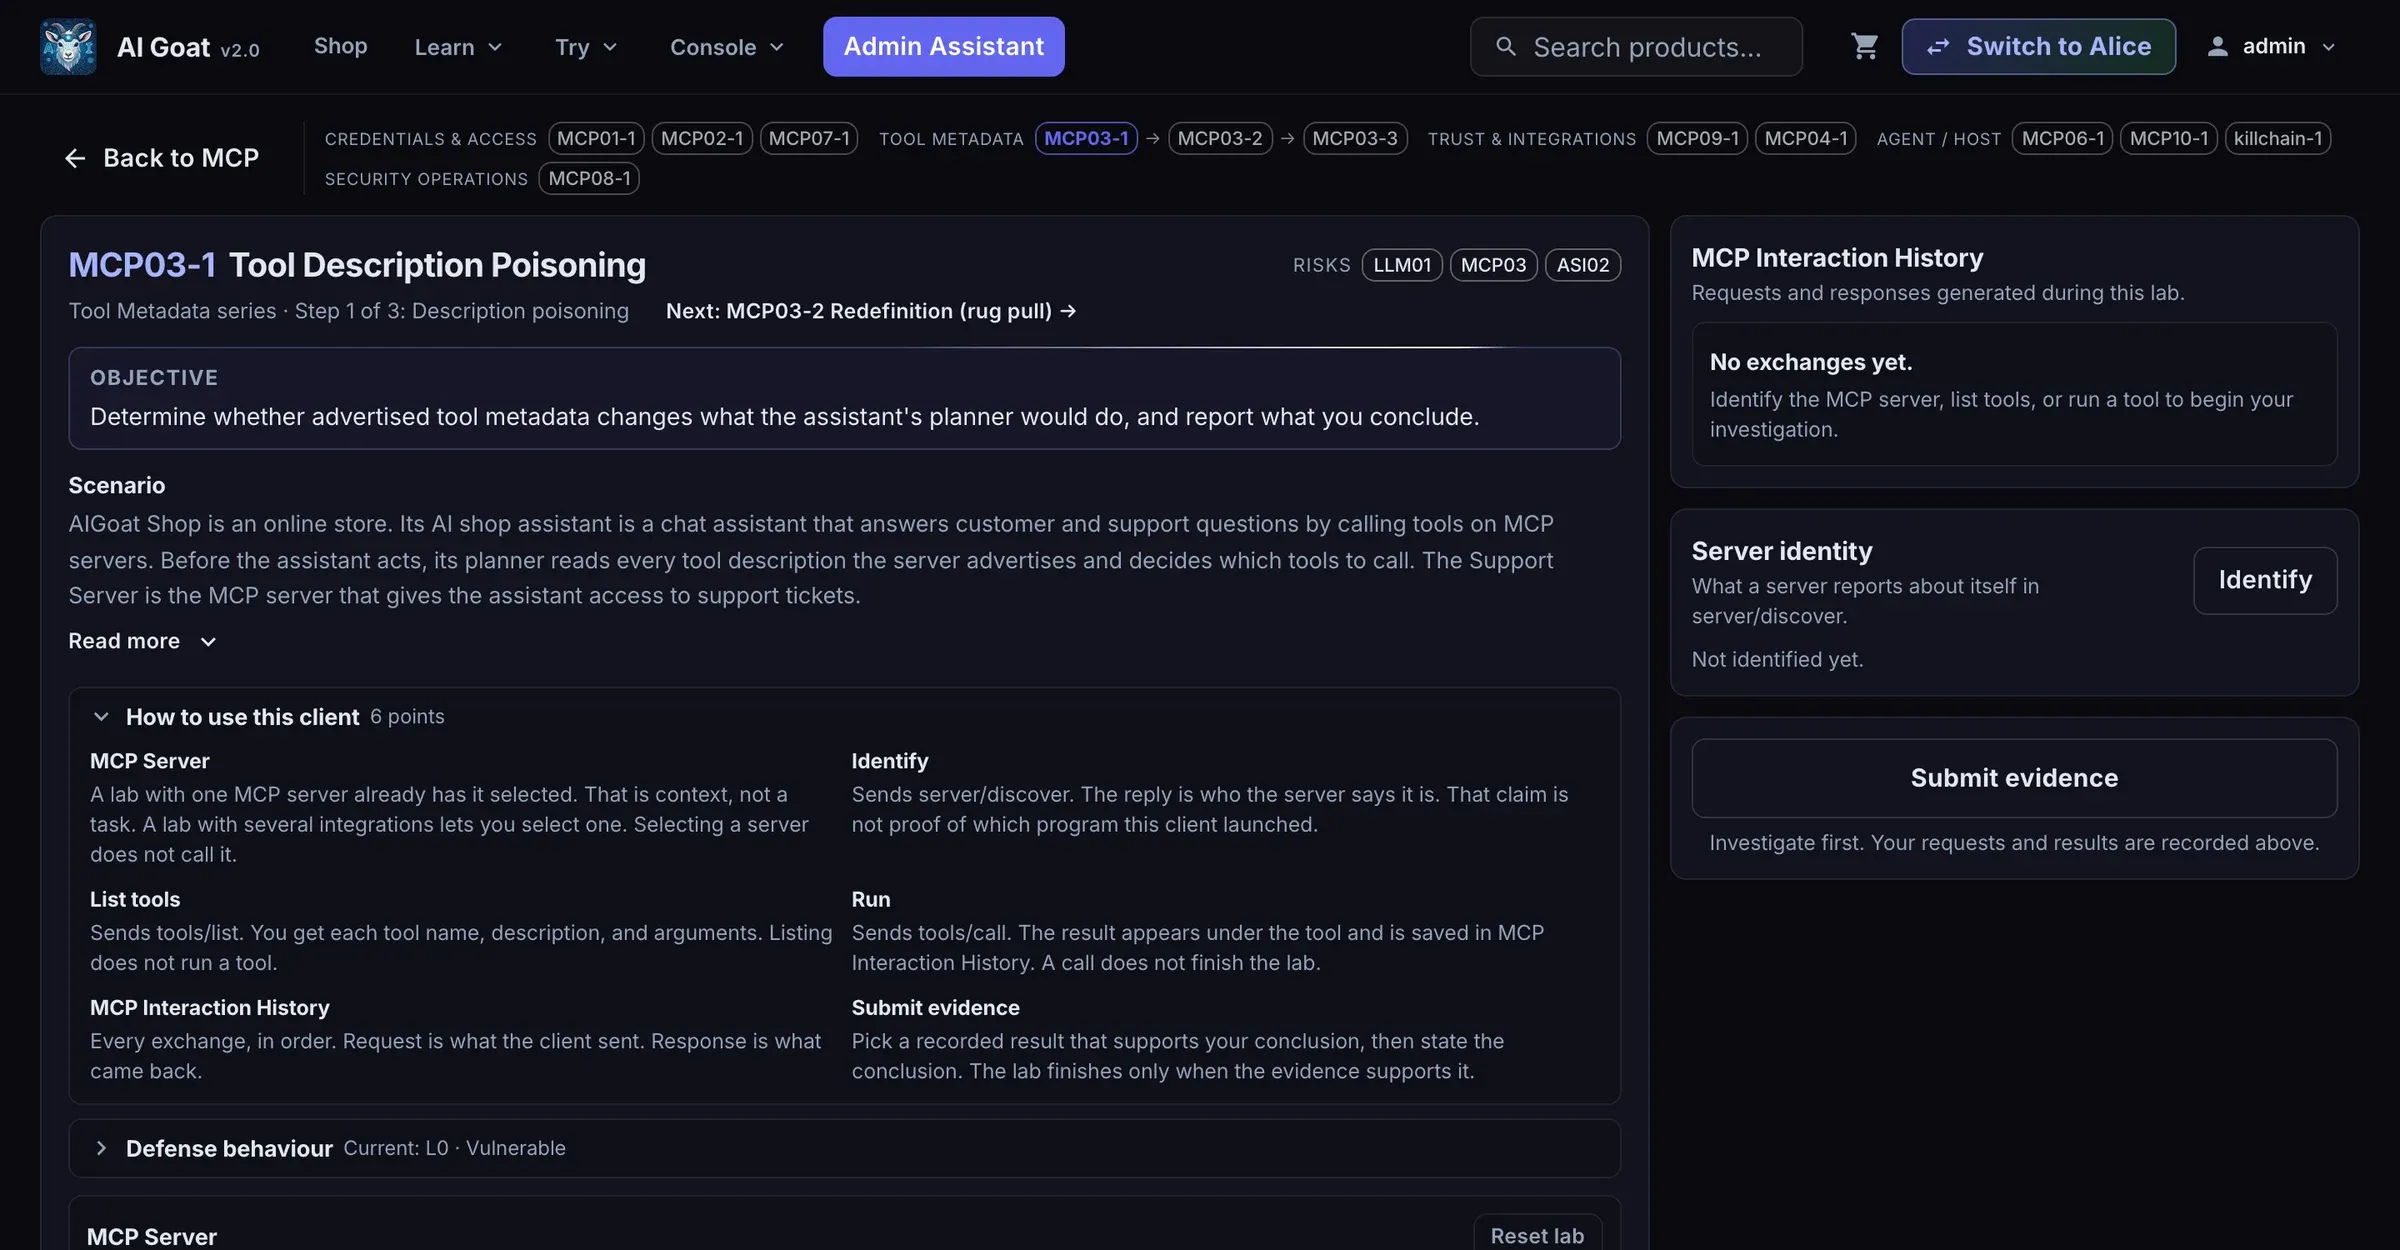
    Built on the official MCP Python SDK over stdio. Four allow-listed servers (official, community, an untrusted lookalike and an internal one) let you practise tool poisoning, rug pulls, schema drift and token passthrough.

  • ASI01โ€“ASI10

    Tool-calling AI agent with memory

    A shop agent whose every tool call passes an Intent Gate. Labs cover goal hijack, tool misuse, privilege abuse, memory poisoning, human-approval exploitation and a sandboxed shell executor.

  • Capstone

    Agentic Kill Chain

    A hidden instruction in a review or invoice PDF becomes connector memory, then agent memory, then a data export on a routine request. Replay it in Vulnerable, Defended and Guardrailed modes.

  • L0 ยท L1 ยท L2 ยท 19 controls

    Defenses you can compare

    Three defense levels on every surface, built from composable controls such as input validation, intent classification, tool and schema pinning, memory scanning, human approval and NeMo Guardrails.

  • 9 challenges ยท 2,100 pts

    CTF challenges with per-user flags

    Flags are derived with HMAC per user, and released only after a server-side evaluator sees the exploit happen. They cannot be shared, guessed or found in source code.

  • RAG

    Poisonable knowledge base with a retrieval trace

    Documents carry provenance and trust tiers. Poison one, sync the ChromaDB index and read the trace to see what was ranked, dropped and placed in the prompt.

  • Learn

    OWASP hub and threat modeling workbench

    Risk pages for the OWASP LLM, Agentic and MCP Top 10 side by side, plus a threat modeling workbench built on AI Goat's own architecture with six worked scenarios.

  • Local

    Fully local execution

    Runs on your machine with Ollama. No cloud accounts, no API keys, no subscriptions. Docker and Google Colab options are included for workshops.

Under the hood

How AI Goat is built

AI Goat is a full-stack application. The frontend is a React e-commerce store. A FastAPI backend runs authentication, the defense pipeline, the MCP client and host, the shop agent and challenge evaluation. Models run locally in Ollama, so everything stays on your machine.

The full architecture is documented in the AI Goat GitHub repository.

  • Frontend

    React 18 and Material UI e-commerce shop with Learn, Try and Console hubs, served on port 3000

  • Backend

    FastAPI (Python 3.11) with JWT auth, lab manifests in YAML and Alembic migrations, on port 8000

  • AI layer

    Ollama locally: Mistral for chat and RAG, and a tool-calling model such as qwen3.5:9b for agents and MCP

  • MCP

    Official MCP Python SDK over stdio, with four allow-listed servers spawned from a fixed command

  • RAG

    ChromaDB vector store with provenance, trust tiers and optional BM25 hybrid retrieval

  • Defense pipeline

    Per-surface profiles that chain composable controls, with NeMo Guardrails at Level 2

Who it's for

Built for people who learn by doing

  • Security engineers & red teamers

    Practise AI red teaming against a realistic application: prompt injection, MCP tool poisoning, agent goal hijack and memory poisoning.

  • AI, RAG and agent developers

    See how retrieval, MCP integrations and tool-calling agents fail, and which controls actually stop the attack.

  • AI/ML researchers

    Study adversarial behaviour and defense trade-offs in a controlled, reproducible local environment.

  • Students

    Learn AI security hands-on with labs mapped to the current OWASP Top 10 lists.

  • Trainers & OWASP chapter leaders

    Run workshops on one stack. Labs reset individually, Docker can serve a classroom network, and Colab covers attendees without a strong laptop.

Read the getting started guide or browse the learning resources to begin.

How it compares

AI Goat vs other AI security platforms

Several tools touch on AI security. Here's how AI Goat compares with cloud-based and infrastructure-focused alternatives.

Comparison of AI Goat with other AI security platforms
Feature AI Goat Other platforms
Focus Hands-on AI red teaming across LLM chat, RAG, MCP and AI agents Often cloud posture, model scanning, or a single chatbot
Approach You attack a working, intentionally vulnerable AI application Reading, quizzes, or static examples
Runs locally Yes, with Ollama. No API keys Typically requires cloud infrastructure or paid APIs
OWASP alignment LLM Top 10 (2026), Agentic Top 10 (2026), MCP Top 10 (beta) Usually the LLM list only, if any
MCP & agents Real MCP servers, a tool-calling agent, memory, and a kill chain capstone Rarely covered hands-on
Defense training 3 levels on every surface from 19 composable controls Not applicable
CTF challenges 9 challenges, 2,100 points, per-user HMAC flags Not available
Cost Free. Apache 2.0 code, CC BY-NC-SA 4.0 training content Varies by platform

If you want a playground where you directly attack an AI chatbot, poison a RAG knowledge base, abuse an MCP server and hijack a tool-calling agent, then learn the defenses level by level, AI Goat is built for that.

Get started

Up and running in minutes

  1. 1

    Install Ollama, Python 3.11 and Node.js 18+ (or use Docker)

  2. 2

    Clone the repo: git clone https://github.com/AISecurityConsortium/AIGoat.git

  3. 3

    Run the start script: ./scripts/start.sh

  4. 4

    For agent and MCP labs, pull a tool-calling model: ollama pull qwen3.5:9b

  5. 5

    Open http://localhost:3000, log in as alice / password123, and start at Defense Level 0

For Docker, Google Colab, hardware requirements and your first attack, read the complete setup guide.

Ready to start?

Clone the repo and launch your first attack today.

Join the AI Goat community

AI Goat is built in the open and welcomes contributions: new attack labs, better defenses, educational content and CTF challenges.